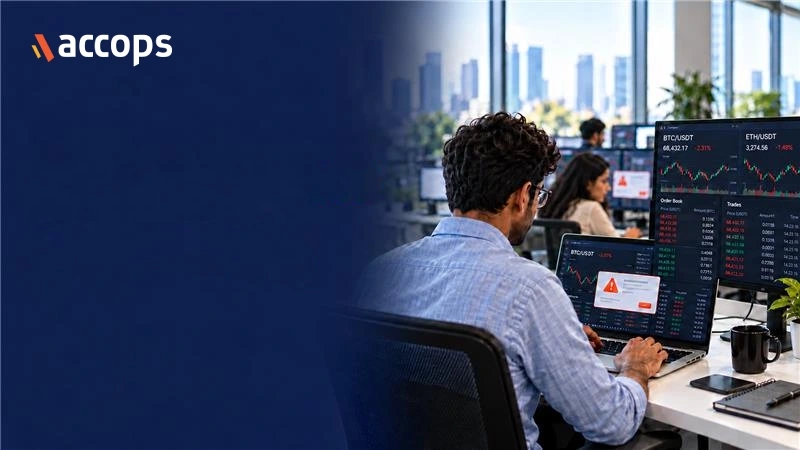
Cyberattacks do not always begin with sophisticated malware or a dramatic breach of the data centre. Sometimes, they begin with a compromised endpoint.
A laptop. A desktop. An administrator workstation. A device that was trusted yesterday and weaponised today.
Recent high-profile incidents show how trusted systems can become attack paths. Sometimes the entry point is an employee’s device. In other cases, attackers exploit third-party services or vulnerabilities in critical infrastructure. What matters is how far that initial access can take them.
The consequences can be devastating.
On 29 October 2026, cryptocurrency exchange Binance suffered a security incident with an estimated impact of around $6.3 billion. In its 30 October update, Binance said its initial investigation suggested that a compromised DevOps engineer’s laptop may have enabled an attacker to access an internal service container and submit unauthorised withdrawal transactions. Binance reported that approximately $3 billion in affected assets had been frozen on-chain. The full attack path remains under investigation, and later reporting has pointed to additional possible points of compromise.
This was not the first major incident in the wider Binance ecosystem. In October 2022, attackers exploited a vulnerability in BNB Chain’s BSC Token Hub cross-chain bridge, resulting in the unauthorised creation of two million BNB tokens, worth nearly $570 million at the time. Unlike the suspected endpoint-related intrusion in 2026, the 2022 exploit targeted the bridge’s verification mechanism. The incidents are distinct, but together they show how different weaknesses can expose high-value systems.
In July 2025, Indian cryptocurrency exchange CoinDCX suffered a breach involving approximately $44 million in an internal operational account. CoinDCX initially reported a server breach; police later said attackers had installed malware on an employee’s company laptop under the pretext of a part-time job. The reported attack path illustrates how a single device with operational access can become a route into sensitive systems.
Similarly, the well-publicised Bybit breach in February 2025 led to losses of nearly $1.5 billion, making it one of the largest digital asset thefts ever reported. Investigations suggested that attackers compromised elements of the transaction approval ecosystem, demonstrating how trusted systems can be manipulated when operational security controls fail.
Although these incidents involved different attack methods, the wider lesson applies equally to banks, manufacturing companies, government agencies, healthcare organisations and enterprises of every size:
When a compromised endpoint has access to sensitive systems, the consequences can extend far beyond that device.
The Real Problem: Trusting Endpoints
Traditional security architectures often assume that endpoints can be trusted once they are connected to the corporate network.
Unfortunately, attackers know better.
Modern ransomware groups and advanced persistent threats target endpoints because they provide a direct path to:
- Privileged credentials
- Sensitive applications
- Internal databases
- Financial systems
- Source code repositories
- Business-critical workloads
A single infected laptop can become the launchpad for a much larger compromise.
A Different Approach: Secure Digital Workspaces
Instead of allowing business applications and data to reside on endpoint devices, organisations are increasingly adopting Virtual Desktop Infrastructure (VDI) and Desktop-as-a-Service (DaaS) models that keep workloads inside secure datacentres or cloud environments.
This is where Accops VDI and DaaS provide a significant security advantage.
With Accops:
- Applications and desktops remain inside the datacentre or cloud.
- Corporate data can remain centrally hosted rather than being stored on user devices.
- Access is governed through Zero Trust principles.
- Multi-factor authentication strengthens identity security.
- Granular policies control clipboard, printing, downloads, and USB access.
- Access from suspicious devices can be blocked to reduce exposure of critical workloads.
- Centralised monitoring improves visibility and incident response.
VDI does not make a compromised endpoint harmless. Attackers may still attempt to misuse an authorised session. However, keeping workloads centrally hosted and restricting data transfers can reduce exposure, particularly when supported by strong authentication, access policies and monitoring.
Security Is No Longer About Prevention Alone
No organisation can guarantee that endpoints will never be compromised.
The more realistic question is:
What happens after an endpoint is compromised?
Organisations that continue to store applications and sensitive information directly on endpoints risk becoming the next headline.
With the right identity, endpoint and session controls, secure digital workspace strategies can reduce the attack surface, restrict unnecessary access to critical systems and improve cyber resilience.
The incidents involving Binance, CoinDCX and Bybit are reminders that cybersecurity is not only about preventing the first intrusion. It is about limiting what an attacker can reach when a trusted device, identity or service has been compromised.
Securing the workspace is therefore as important as securing the network. Accops VDI and DaaS help organisations keep critical applications and data centrally managed, apply access controls and reduce the potential impact of an endpoint compromise.